Jamio lowcode nocode cloud platform

PRESIDIO | Adequate Assets

Adequate Assets: Can you demonstrate what you're doing?

PRESIDIO | ADEQUATE STRUCTURES

Presidio is the tool for planning, verifying, documenting, and monitoring the activities a company uses to establish the appropriate structures required by art. 2086 of the Italian Civil Code, making the path undertaken demonstrable over time. A cloud service on the Jamio openwork platform , provided in collaboration with LUM Enterprise .

The service is eligible for the MIMIT Cloud & Cybersecurity Voucher, covering up to 50% of eligible expenses.

It's not enough to decide. You need to be able to demonstrate the path.

A DUTY FOR EVERY SOCIETY

Article 2086 of the Civil Code requires the establishment of organizational, administrative , and accounting appropriate to the nature and size of the company, including for the timely detection of crises, within the framework of the Corporate Crisis and Insolvency Code.


DECISIONS ARE NOT ENOUGH

It is necessary to be able to reconstruct checks, responsibilities, and interventions: what was evaluated, what was decided, what was done.


A RECONSTRUCTABLE PATH

Presidio does not automatically certify suitability: it makes the path undertaken by the company reconstructable and demonstrable over time.

Jamio and LUM Enterprise

Request your business check-up

Jamio for adequate organizational structures

A cloud service on the Jamio openwork platform

Presidio | Adeguati Assetti is provided by Openwork on the Jamio SaaS platform, in collaboration with Enterprise. It is the environment where the company organizes assessments, controls, evidence, documents, responsibilities, and critical issues, and manages deadlines and planned actions. A dashboard provides a comprehensive view down to the details of each individual control.

Configurable in the future for other compliance areas as well.

Plan

Define the necessary actions, priorities, responsibilities, and deadlines.

Check

Assessment of 233 controls in 13 government areas.

Document

Collect evidence and results of checks, control by control.

Monitor

Track the status of actions, periodic checks, and critical issues over time.

Qualifications and security: Openwork reports the ACN QC2 qualification for the Jamio SaaS service and indicates ISO/IEC 27001, 27017 and 27018 certifications. Consult the manufacturer's references.

From the overview to the single control

Assessment: 233 audits organized across 13 governance areas.
Evidence: Documents and audit results collected on a control-by-control basis.
Actions: Priorities, responsibilities, and deadlines associated with planned activities.
Monitoring: A dashboard to track critical issues and progress, down to the detailed audit details.

233 Presidium checks

Assessment of 233 controls across 13 governance areas. For each control, Presidio organizes evidence, responsibilities, deadlines, and progress.

4 states, an overview

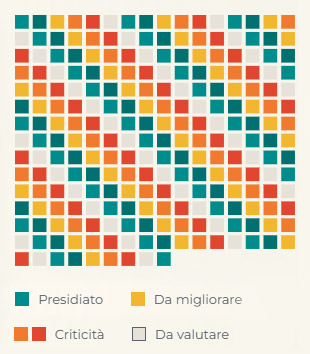
Monitored, needs improvement, critical issues, needs evaluation: the diagram allows you to track checks and actions over time.

In the image on the right, each square is a control.
The diagram does not represent the results of a single company.

Adequate Controls Organizational Structures
The 233 Presidio checks

Presidio organizes evidence, responsibilities, deadlines, and planned actions, allowing you to monitor their status over time. Decisions and implementation remain with the company. 

The 13 areas

1) Governance 2) Administration and accounting 3) Planning and control 4) Orders and margins 5) Treasury 6) Active and passive cycle 7) Commercial 8) Operations 9) Human resources 10) Risks 11) Early warning 12) Remediation 13) Data quality

One service, four perspectives

Administrator

Demonstrate the path taken to equip the company with adequate assets.

Board of Directors

Make decisions based on documented checks and monitor the implementation of interventions.

Board of Auditors

Have evidence of the company's audits and actions to support supervision.

Auditor

Find evidence relevant to your audits.

The service is eligible for the Cloud & Cybersecurity Voucher

If the company meets the requirements and the conditions set out in the notice are met, the provision of Presidio (24-month subscription and related services) can benefit from the MIMIT Cloud & Cybersecurity Voucher. The provider and services must be listed in the MIMIT list.

50%

Non-repayable contribution on eligible expenses

20.000 €

Maximum contribution

4.000 €

Minimum spending plan

€150 million

Endowment, of which approximately 71 million reserved for the South

Subject to verification of the requirements, applicable conditions and availability of resources.

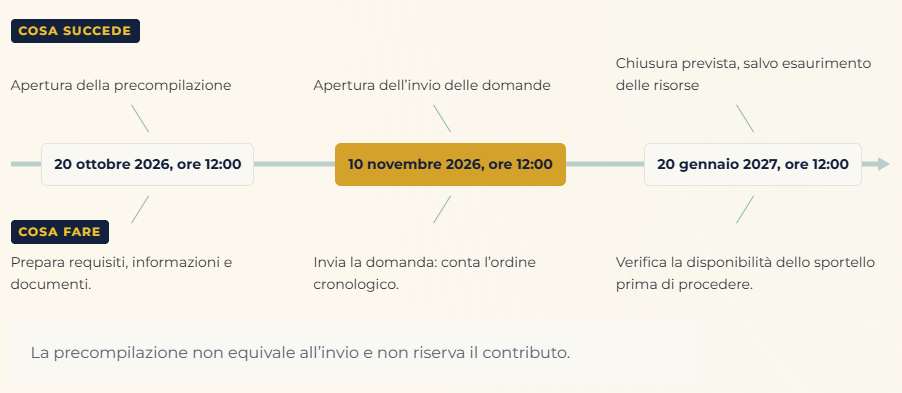
Cloud & Cybersecurity Voucher: the dates

For the board of auditors and auditors

Audits and evidence, traceable over time. Presidio organizes controls, evidence, responsibilities, deadlines, and the progress of the company's planned actions. The board of statutory auditors can use information relevant to its supervisory activities; the auditor uses information relevant to the audits under his or her responsibility. Distinct roles, evidence traceable over time.

Information to consult over time

Controls and evidence: Documentation organized to track audits and locate relevant information.
Responsibilities and deadlines: An overview of the company's planned actions, those responsible, and the expected timelines.
Progress: Information on the actions to be taken and documented activities.

The board of statutory auditors uses information relevant to oversight; the auditor uses information relevant to their audits. The information organized by the service supports the professionals' work: assessments and conclusions remain their responsibility.

The announcement in detail

MIMIT measure “Cloud & Cybersecurity Voucher” · Ministerial Decree 18 July 2025 · DD 4 August 2026.

SMEs and self-employed workers from across Italy. To assess the size of SMEs, also consider associated and affiliated companies. The budget is €150 million. Approximately €71 million is reserved for Abruzzo, Basilicata, Calabria, Campania, Molise, Puglia, Sardinia, and Sicily.

The contribution is de minimis. The plan must be at least €4,000. Only one application per applicant is allowed.

– Cybersecurity hardware and software.

– IaaS infrastructure cloud and PaaS platform.

– SaaS software: accounting, HR, ERP, CRM, e-commerce, and collaboration.

– Related configuration, monitoring, and support, within 30% of the plan.

Suppliers and services must be listed on the MIMIT list. Solutions must be new or more advanced than those already in use.

In direct purchases, expenses must be incurred within 12 months of the grant.

The subscription lasts at least 24 months. Fees for the first 24 months are eligible.

The signature must take place after the application has been sent and within 30 days of the granting.

Subscription notification must be made within 60 days, otherwise it will expire.

Only expenses incurred after the application has been submitted are eligible.
– Solutions equivalent to those already in use.

– Updates without substantial improvements.

– Simple license extensions or seat increases.

- Training.

Consulting is not admissible.

– Self-certification with company details, certified email address, location of the intervention, and requirements.

– Connectivity contract with at least 30 Mbps download speed, already active upon application.

– Description of the starting situation and the expected improvement.

– Supplier offers with service codes and cost items.

– Declaration on the catastrophe insurance policy.

Also check the de minimis capacity and prepare the access and digital signature tools.

The company or self-employed worker submits the application online, directly or through a delegate, using SPID, CNS, or CIE and a digital signature.

The application process is open to the public, in chronological order, until resources are exhausted. Each applicant may submit only one application.

Pre-filling is not equivalent to submitting and does not reserve the contribution.

The grant arrives after the expense. You can request payment no earlier than three months after the grant is granted, in one or two installments.

Payment is made after verification, within 60 days of the request. Evaluate the funds required to cover expenses in advance.

Request your business check-up